|
AES-256 AT REST · TLS 1.3 IN TRANSIT
|
HIPAA-READY
|
SOC 2 TYPE II AUDIT UNDERWAY
Every session is cryptographically logged. Your security team has complete visibility — in real time.
Governed before the first line runs.
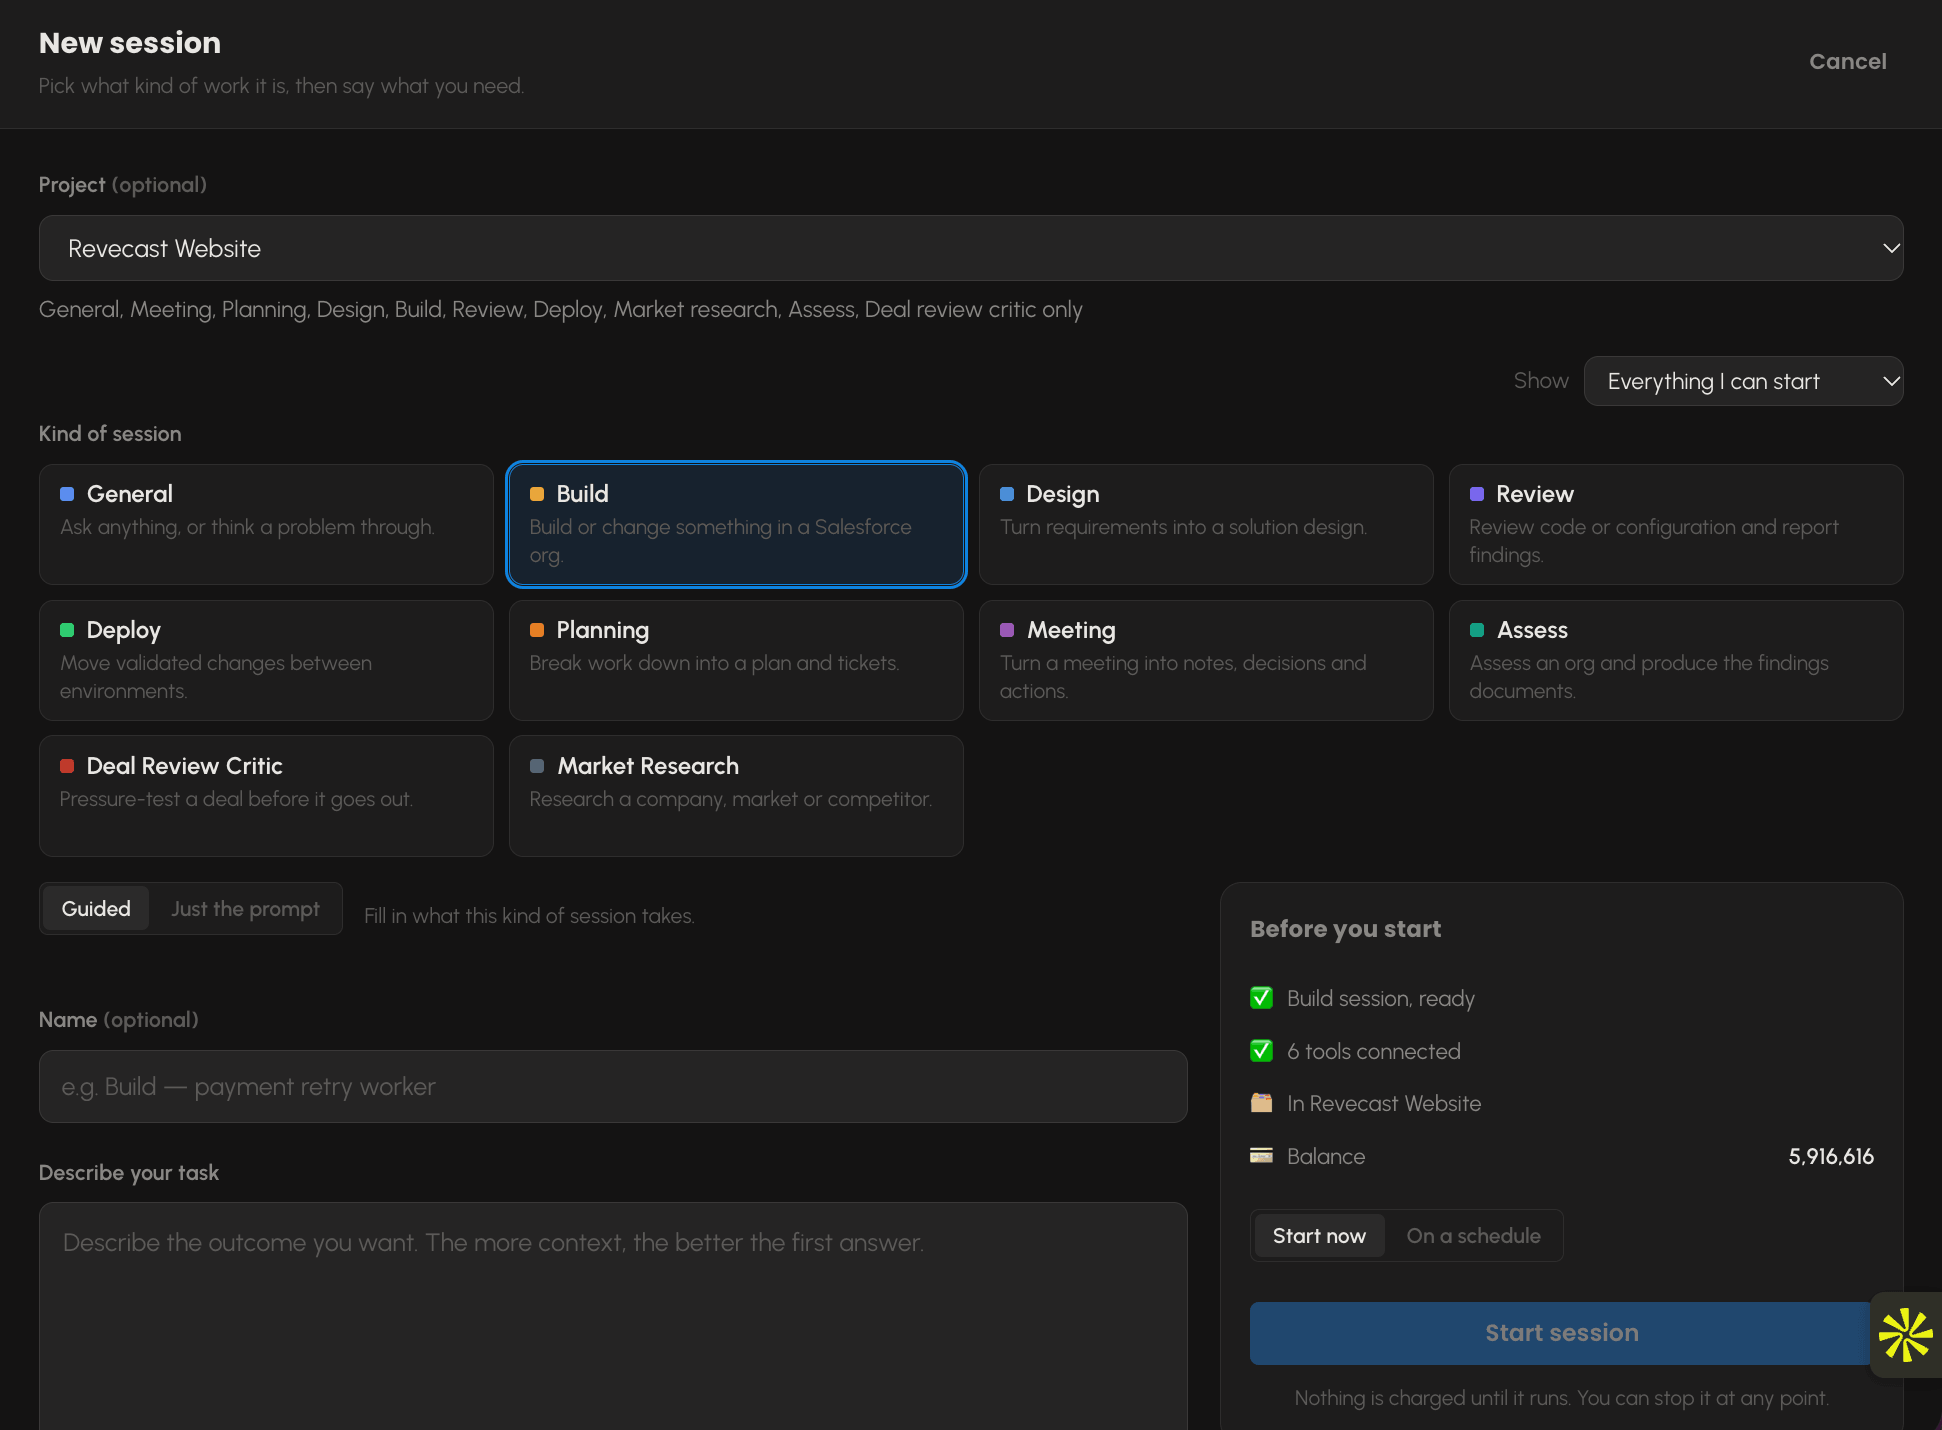
The “Before you start” panel isn’t UX — it’s governance. Every session confirms connectors, validates permissions, and opens an immutable audit log before Orchestrate does anything.
Four layers. No shortcuts.
Zero-Trust Session Model
No data persists between sessions.
Credentials scoped per session and discarded on close. Every tool call, input, and output captured to an immutable audit trail. No cross-org data leakage — your metadata never leaves your session boundary.
Data & Privacy
Your data is never used to train AI.
Session data not stored beyond your configured retention window. OAuth credential handling — we never see your password. No model training on customer data. Ever.
Compliance
Built for regulated environments.
HIPAA-ready: BAAs available for Enterprise plans.
FERPA-capable: Designed for higher education environments.
SOC 2 Type II: Audit in progress.
CCPA/GDPR: Data practices aligned with California and EU privacy frameworks.
Access & Identity
Plugs into your existing infrastructure.
SSO via SAML 2.0 / OIDC. Role-based session access controls. MFA enforced on all accounts. IP allowlisting on Enterprise plans. Full audit logs accessible to your security team.
What we never do.
Store or log plaintext credentials
Use your session data to train, fine-tune, or evaluate AI models
Allow data from one organization to influence sessions in another
Execute destructive operations without an explicit human confirmation gate
Write to production systems without a human-approved deploy step
Questions about security?
Security documentation is available to enterprise prospects. BAA requests, compliance questionnaires, and enterprise security reviews — reach out directly.